Web3 Nodes
Decentralized Storage Nodes: How Filecoin and IPFS Preserve Web3 Data
Learn how Filecoin storage nodes work, from Proof of Replication (PoRep) to sealing pipelines, hardware requirements, collateral staking, and retrieval latency.
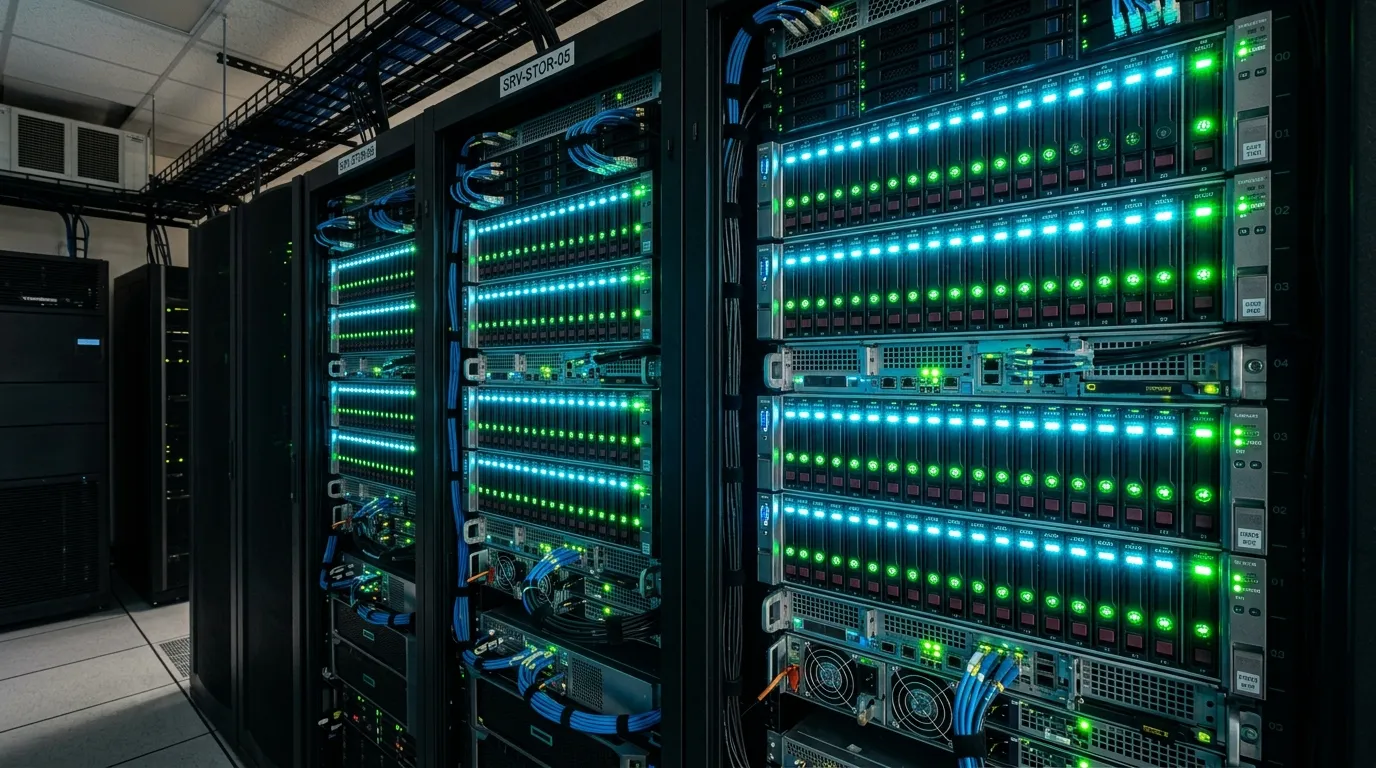
Decentralized storage is the bedrock of non-custodial Web3 architecture. While standard blockchains excel at validating state changes and smart contract execution, storing gigabytes or terabytes of arbitrary data directly on a layer-1 ledger is prohibitively expensive. Networks like the InterPlanetary File System (IPFS) and Filecoin provide the data availability, content addressing, and verifiable persistence layer that decentralized applications (dApps), NFT metadata, and blockchain archives require.
However, operating a decentralized storage node is fundamentally distinct from hosting a simple full node or validator. It demands dedicated enterprise storage arrays, high-throughput GPU sealing pipelines, and cryptographic collateral. This technical guide explains how storage providers (SPs) operate, the mechanics of cryptographic storage proofs, and the realities of running storage hardware.
If you are just beginning your node exploration journey, consult our beginner’s guide to running nodes or our breakdown of the best crypto nodes for beginners.
IPFS vs. Filecoin: Content Addressing vs. Verifiable Persistence
A common point of confusion in Web3 storage is the architectural relationship between IPFS and Filecoin:
- IPFS (InterPlanetary File System) is a peer-to-peer hypermedia protocol. It assigns data a unique Content Identifier (CID) derived cryptographically from a SHA-256 hash of the content itself. Anyone requesting the CID retrieves the exact bytes regardless of where they are hosted. However, IPFS alone has no economic incentive layer: if nodes garbage-collect or stop pinning the CID, the data disappears from the peer network.
- Filecoin introduces the incentive and verification layer atop content-addressed storage. Storage Providers (SPs) enter cryptographic deals with clients, post collateral in FIL tokens, and generate automated zero-knowledge proofs demonstrating that they continuously retain and serve the exact data over time.
The Cryptographic Proving Pipeline: PoRep and PoSt
How does an open peer-to-peer network verify that an independent node operator across the world is genuinely holding a client’s files, without requiring someone to download the entire file repeatedly? Filecoin solves this using two novel cryptographic proof systems:
- Proof of Replication (PoRep): Proves that a Storage Provider has created a unique, dedicated physical copy of the data (replicating it into a sealed sector) rather than deduplicating multiple copies into a single shared drive.
- Proof of Spacetime (PoSt): Continuously proves that the provider still retains that identical replica over an extended duration. Every 24 hours, the blockchain challenges providers with randomized queries (WindowPoSt) that must be answered with zk-SNARK cryptographic proofs within strict block deadlines.
+-------------------------------------------------------------+
|                Filecoin Sector Sealing Pipeline             |
+-------------------------------------------------------------+
|  1. PreCommit 1 (PC1) : CPU-bound SDR graph generation       |
|  2. PreCommit 2 (PC2) : Column hashing & Merkle tree build  |
|  3. Commit 1 (C1)     : Proof synthesis phase               |
|  4. Commit 2 (C2)     : GPU-accelerated zk-SNARK generation |
+-------------------------------------------------------------+
Hardware Requirements for Storage Providers
Operating a viable Filecoin storage provider requires substantially more compute and disk throughput than standard proof-of-stake validators. Storage providers separate their operations into two functional clusters:
- Sealing Workers: Compute-dense machines equipped with multi-core CPUs (AMD EPYC or Ryzen with SHA extensions), at least 256 GB to 512 GB of RAM, high-speed NVMe scratch drives (for scratch calculations), and enterprise GPUs (such as RTX 3090, 4090, or A6000) specifically used to compute zk-SNARKs during the Commit 2 phase.
- Storage Arrays (Lotus Storage): Enterprise JBODs (Just a Bunch of Disks) connected via SAS/HBA controllers, configured in robust ZFS RAIDZ2 or RAIDZ3 pools providing tens or hundreds of terabytes of durable raw capacity.
| Component | Minimum Production Spec | Recommended Scaling Spec |
|---|---|---|
| CPU | 8+ Cores (AMD Zen 3+ with SHA extensions) | Dual AMD EPYC 32+ Cores |
| RAM | 128 GB ECC RAM | 256 GB – 512 GB ECC RAM |
| GPU | 1x NVIDIA RTX 3080/3090 (16GB+ VRAM) | 2x NVIDIA RTX 4090 or A6000 |
| NVMe Cache | 2 TB Gen4 NVMe (High Endurance TBW) | 2x 4 TB NVMe U.2 Enterprise SSDs |
| Long-Term Storage | 100 TB Enterprise SAS/SATA HDD array | 500+ TB ZFS JBOD Enclosures |
| Network Uplink | 1 Gbps symmetrical dedicated fiber | 10 Gbps redundant uplinks with static IPv4 |
Retrieval Latency and Decentralized Content Delivery
While decentralized storage excels at immutable permanence and verifiable retention, raw retrieval times from cold sealed sectors are typically slower than centralized Content Delivery Networks (CDNs) like Cloudflare or Amazon CloudFront.
To bridge this gap, modern Web3 infrastructure employs hybrid caching architectures:
- Unsealed Copies: Fast-access local copies stored in hot NVMe caches for popular files.
- Decentralized CDNs (Saturn / Titan / IPFS Gateways): Distributed edge nodes that cache popular IPFS CIDs close to end users, serving Web3 assets in milliseconds while relying on the underlying Filecoin network as the verifiable archive.
Decentralized Storage Pros
- Cryptographic content addressing eliminates broken links and censorship
- Verifiable retention guarantees backed by zero-knowledge math
- Competitive open-market pricing compared to AWS S3 storage tiers
- True sovereign ownership of application state and user data
Decentralized Storage Cons
- High initial capital expenditure for GPU sealing and NVMe caching hardware
- Substantial initial token collateral requirements to accept client deals
- Cold sector unsealing introduces latency compared to centralized CDNs
- Complex administrative overhead managing ZFS pools and Lotus daemons
Frequently Asked Questions
- Can I run a Filecoin storage node from home?
- While technically possible for testing on Calibration testnet, operating a mainnet storage provider on residential broadband is strongly discouraged. Sector sealing requires hundreds of gigabytes of RAM, high-end GPUs, sustained disk I/O, and strict 24/7 uptime to avoid collateral slashing.
- What is the difference between an IPFS node and a Filecoin node?
- An IPFS node stores and shares content-addressed data on a peer-to-peer basis without economic incentives. A Filecoin node is an economic actor that takes on binding storage contracts, stakes crypto collateral, and submits recurring cryptographic proofs (PoRep/PoSt) to earn deal payments and block rewards.
- How does Filecoin prevent fake storage claims?
- Through Proof of Replication (PoRep). The sealing algorithm transforms raw data into a unique, encrypted format tied specifically to the provider's cryptographic key and sector ID. This prevents nodes from claiming to store the same file across multiple IDs without dedicating real physical capacity.
- What happens if a drive in my storage array fails?
- Enterprise providers configure storage in fault-tolerant arrays (such as ZFS RAIDZ2 or RAIDZ3). If an individual drive fails, the pool reconstructs data from parity disks. If an entire sector is lost and cannot be recovered before the next WindowPoSt challenge, that sector is declared faulty and collateral is slashed.
Bottom Line
Decentralized storage is one of the most mature pillars in Web3 infrastructure, replacing corporate trust with verifiable mathematical proofs. While running a storage provider requires serious enterprise hardware and rigorous uptime monitoring, understanding its underlying cryptographic mechanics—from content-addressed CIDs to zero-knowledge spacetime proofs—is essential for any engineer navigating Web3 and DePIN networks.
For more infrastructure tutorials, check out our guide to Solana validator hardware and our walkthrough of Ethereum validator staking.
This article is for educational purposes only and should not be considered financial or investment advice. Always conduct your own research (DYOR) before investing in cryptocurrencies or deploying hardware infrastructure.